Attack range
Kali → Windows/AD and vulnerable Linux targets on an isolated 10.10.10.0/24. Curated scenarios, reviewed plans, real commands, hard scope guard.
Real Kali → Windows attacks, real detection telemetry, real evidence. A local cyber range that shows its work.
Kali → Windows/AD and vulnerable Linux targets on an isolated 10.10.10.0/24. Curated scenarios, reviewed plans, real commands, hard scope guard.
Windows Security/System/PowerShell, Kali journal and Suricata IDS in one timeline. Versioned rules, source health, explicit limits.
15 live assets, 10 control mappings across NIST/CIS/ISO with honest gaps, detection evidence and JSON/Markdown export.
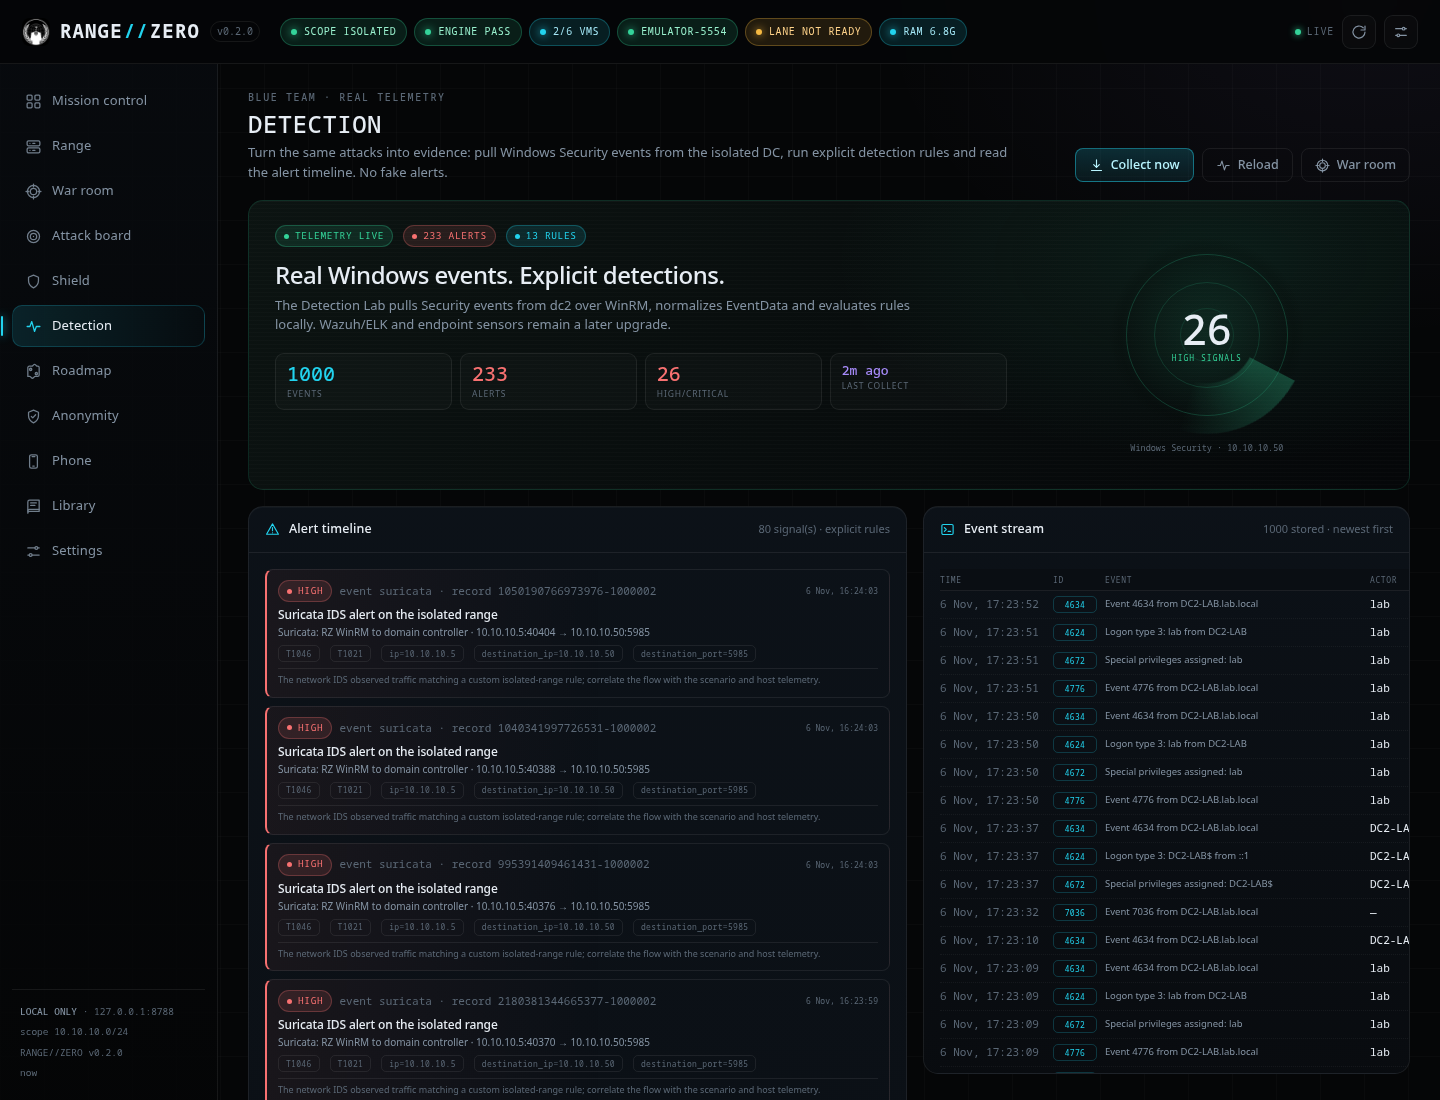 LIVE DETECTION LAB · 13 RULES
Six live channels, high-signal sorting, source health and a 1,000-event evidence window. The range shows what it detected — and what it did not.
No anonymity guarantee. The lab is isolated; identity safety is a separate, verified lane.
Practice only against the isolated lab or systems with written authorization.
No accounts/MFA, multi-tenancy, SLA or external audit yet. This is a private pilot.
Zero-budget pilot. No waitlist data on this design preview; the public landing is separate.